ASE Cloud Services Chatbot Interface


Find out in 5 to 10 minutes how prepared your organisation is for safe, responsible and sovereign AI.
Free, no account needed · Six domains · Your provisional score straight away
Start the assessment →The Sovereign AI Readiness Assessment from ASE Cloud Services measures, across six domains, how ready your organisation is to use AI responsibly and independently. Your data stays in the EU, no tracking cookies are placed and the result is a management-level stocktake, not a legal opinion.
The problem
They stall on governance, data quality, security, dependence on suppliers outside the EU and unclear responsibilities. Most AI checks look only at productivity.
What this assessment does differently
Sovereignty (where your data and models run), AI Act classification, GDPR and data management, workplace security, accessibility and implementation readiness. In practice, these cannot be judged in isolation from one another.
What you get out of it
A score from 0 to 100, your strengths, your biggest gaps, the sector context and one primary next step. Choose the short version (14 questions, about 4 minutes) or the full version (28 questions, about 8 minutes). “I don’t know” is a valid answer and counts as a finding, not as a zero.
Choose the short or the full version, answer the questions and see your provisional score and your main areas for attention straight away. You then receive the full management report by email (pdf), at the business email address you provide. While you are completing the assessment, your answers are held only in your own browser.
Is the assessment not working in this window? Open the assessment in a new window.
The domains are not weighted equally. AI governance and data sovereignty count the most, because that is where the legal and contractual risks lie.
Domain 1 · weighting 22%
In which jurisdictions are your AI data, embeddings, logs and backups processed? How dependent are you on non-European hyperscalers for critical processes? Is there a tested exit strategy, and do you have sight of concentration risk and subcontracting in the supply chain (NIS2)?
Domain 2 · weighting 26%
Is there a central AI register, including employees’ own use of AI? Have roles been assigned for ownership, risk, privacy, security and human oversight? Do you know the risk category of each application, has AI literacy been organised (Article 4) and do you meet the transparency obligation in Article 50, including machine-readable marking?
Domain 3 · weighting 16%
Has it been decided in advance which personal data, confidential data and intellectual property AI may process? Have data flows, retention periods, sub-processors and transfers been documented for your Article 30 record and your data protection impact assessments (DPIAs)? Is training on your data contractually excluded?
Domain 4 · weighting 16%
Central identity and access management with MFA and periodic review (for public bodies the national baseline for government, for NIS2 entities the national NIS2 implementation), endpoint security, management of cryptographic keys, logging and monitoring of AI interactions with a working reporting process, and independent testing for AI-specific vulnerabilities.
Domain 5 · weighting 15%
Is your internal knowledge up to date and structured well enough for AI to work with? Are there clearly scoped processes with a baseline measurement? How do you check the quality of AI output, and are your AI channels accessible to WCAG 2.2 AA, as required by the EU Web Accessibility Directive and the European Accessibility Act?
Domain 6 · weighting 5%
Is there a programme with an executive sponsor, an owner and priorities for the next twelve months? Timing and budget do not count towards your maturity score, but they do determine your Implementation Readiness and which next step we recommend.
Straight after the last question you see your provisional score and your three main areas for attention. If you request the full management report, you receive the following by email as a pdf:
An overall score from 0 to 100, a score per domain and a coverage indicator showing how much of the result rests on “I don’t know”.
Your strengths, your biggest gaps and, for each gap, a concrete first step you can discuss internally.
What the result means for your sector: local, regional or national government, healthcare, education, social housing, financial or business services, industry, non-profit.
Statutory deadlines that affect you, such as the marking obligation of 2 December 2026 for generative AI, and organisational blind spots.
Low, medium or high: can your organisation turn the insights into action now? This signal is separate from your maturity score.
One primary recommendation based on your biggest gap, with a secondary option, plus an overview of all your answers to discuss internally and repeat later.
As soon as sufficient data is available, you will be able to benchmark your score against organisations in your sector.
The benchmark is built from anonymised assessment results within your sector.
For board members, senior management, IT managers, CISOs, privacy officers and policy advisers who want to use AI without losing control of data, costs and responsibilities. The assessment suits organisations that:
Work with personal data or make decisions about people.
Local, regional and national government, executive agencies, healthcare, education, social housing.
Fall under the AI Act, the GDPR, NIS2 or national government baselines for information security.
Or need to demonstrate to clients and regulators that AI is being used in a controlled way: financial and business services, industry.
Depend on non-European cloud or AI platforms.
And want to know how realistic a European or sovereign alternative is for them.
Are already experimenting with AI.
But have not yet set up a central register, a risk process or ownership.
The questions can be answered without a technical background. If you complete the assessment together with IT, privacy and the business, you get the most complete picture.
ASE Cloud Services helps organisations use AI while retaining sovereignty: data, models and workplaces within the EU, under European law and the GDPR, with control in your hands. We combine that sovereign infrastructure with expertise in AI governance, the AI Act, ISO/IEC 42001, information security and digital accessibility.
Our management system is certified to four ISO standards: ISO/IEC 27001 (information security), ISO/IEC 27701 (privacy), ISO/IEC 42001 (AI management) and ISO 9001 (quality). We use the same standards as the yardstick in this assessment. The result deliberately does not steer you towards a single product, but towards the next step that fits your biggest gap: an ISO/IEC 42001 GAP Assessment, the ASE Sovereign Workplace, the AI Adoption Programme or a conversation with an ASE expert.
While you are completing the assessment, your answers stay in your own browser. Only when you click “Send my report” are your business details and the result sent to our own server within the EU. The assessment is a management-level stocktake, not a legal opinion.
We use your details to link the report to your organisation and send it to you by email, and we keep them for a maximum of 24 months after the last contact. We only contact you about the outcome if you give separate consent for that. We use aggregated, anonymised scores for the sector benchmark; no organisations or individuals can be identified from them. The spam protection is self-hosted and places no cookies. See the privacy statement.
The outcome does not replace a data protection impact assessment (DPIA), legal review, security audit or formal AI Act classification. Legal references are current as at 5 September 2026 and take account of the Digital Omnibus, Regulation (EU) 2026/1744. If you want a formal review, take a look at the ISO/IEC 42001 GAP Assessment.
Want to know where your organisation stands? The assessment is free, takes 5 to 10 minutes and gives you your provisional score straight away. If you would rather talk it through first, book a free 30-minute consultation.
Start your AI Readiness Assessment →A sovereign AI readiness assessment is a self-assessment that maps how ready your organisation is to use AI both responsibly and independently. The assessment from ASE Cloud Services tests six domains: data sovereignty, AI governance and AI Act classification, privacy and GDPR, workplace security, knowledge, quality and accessibility, and implementation readiness. You immediately receive a score from 0 to 100, a score per domain, three priorities and an Implementation Readiness signal.
The short version has 14 questions and takes about 4 minutes; the full version has 28 questions and takes about 8 minutes. Straight after the last question you see your provisional score and your main areas for attention. The full management report contains your score per domain, a coverage indicator, three concrete priorities, the sector context, AI Act and governance points for attention, your Implementation Readiness and one recommended next step. You can print the report or save it as a PDF, and you also receive it by email.
No. The assessment is an initial management-level stocktake. A high score does not automatically mean that you comply with the AI Act or the GDPR, and the result does not replace a data protection impact assessment (DPIA), legal review, security audit or formal risk classification under the AI Act. The legal references are current as at 5 September 2026 and take account of the Digital Omnibus.
While you are completing the assessment, your answers stay in your own browser. Only when you click “Send my report” do we send your business details and the result to our own server within the EU, so that we can link the report to your organisation and send it to you by email. We keep the data for a maximum of 24 months after the last contact and only get in touch if you give separate consent for that. See our privacy statement.
For board members, IT managers, CISOs, privacy officers and policy advisers in local, regional and national government, executive agencies, healthcare, education, social housing, financial and business services, and industry. The questions are worded so that you can answer them without a technical background; “I don’t know” is a valid answer and counts as a finding, not as a zero.
The readiness assessment is a free self-assessment of no more than eight minutes that points you in the right direction. The ISO/IEC 42001 GAP Assessment is a guided engagement in which we test your AI management system against the standard, with interviews, document review and a report with priorities. If you score below 65 on AI governance in the readiness assessment, the GAP Assessment is the logical next step.
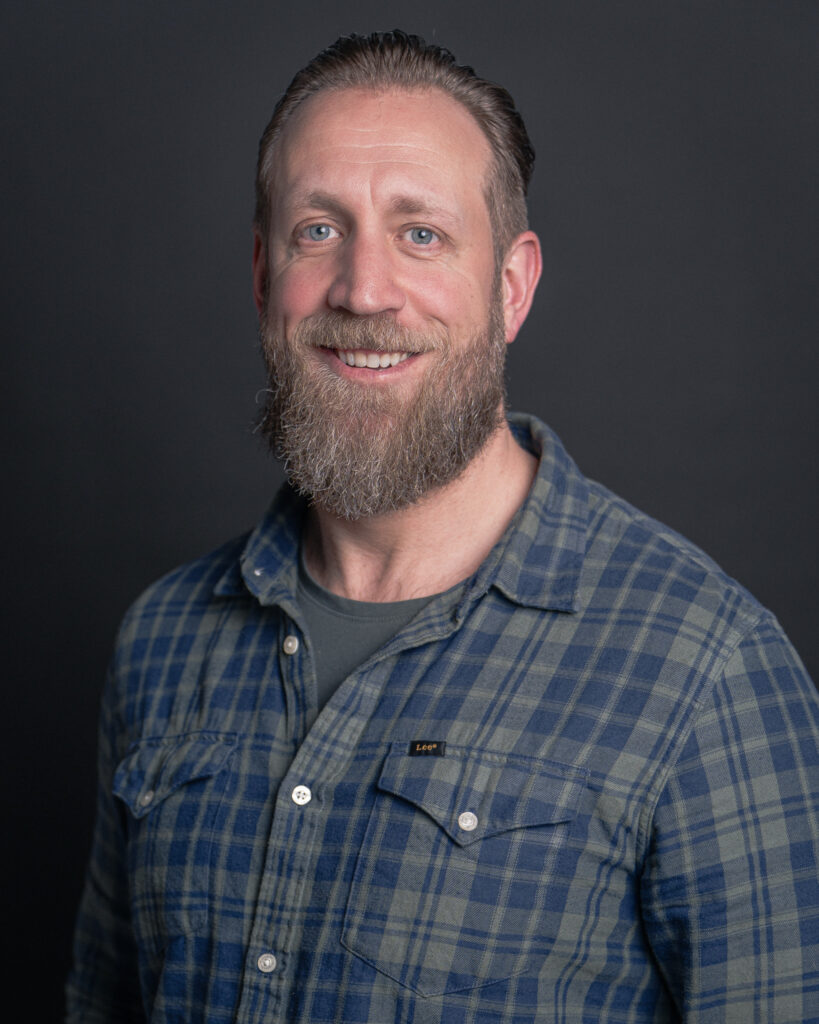
Alain van Zwol
Founder of ASE Cloud Services
Alain van Zwol is the founder of ASE Cloud Services and works daily on European, GDPR-compliant cloud and AI solutions. Through ASE, he guides organisations in their transition to a sovereign workplace free from dependence on US tech giants. You can read more about Alain and the team on the about-us.
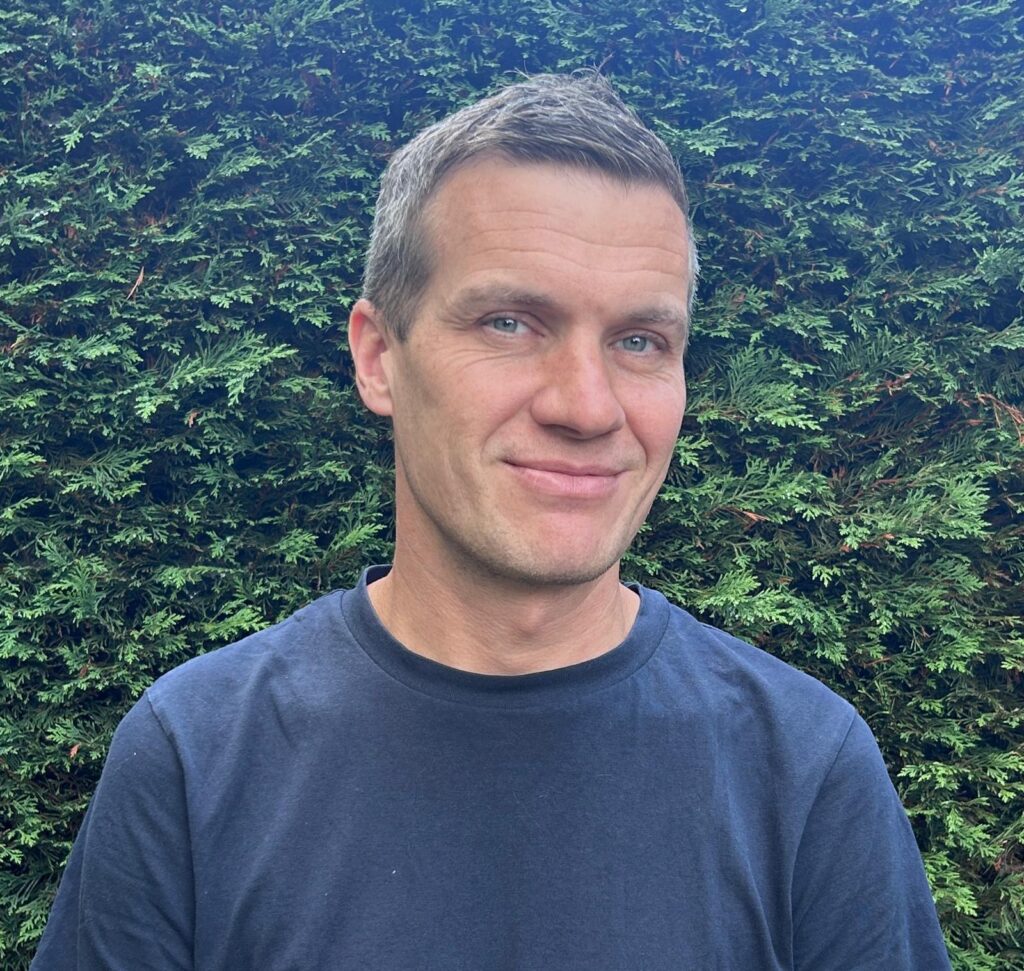
Sebastiaan Hoogeveen
Co-founder of ASE Cloud Services
Sebastiaan Hoogeveen is co-founder of ASE Cloud Services and combines his background as a mechanical engineer with advanced expertise in AI engineering. His experience with C++ during his studies provides a strong technical foundation for his work as an AI engineer. Calm, precise, and composed, he likes to keep an overview. As a team player and connector, he translates complex technology into practical AI solutions. Learn more about Sebastiaan and the team on the About Us page.